A cybersecurity program for small businesses typically includes risk assessment, security policies, employee training, technical controls like endpoint protection and MFA, data backup and recovery, and an incident response plan. It also includes ongoing monitoring, vendor management, and periodic testing to keep defenses current. The goal is practical risk reduction...
How to Identify and Prioritize IT Risks in Your Business
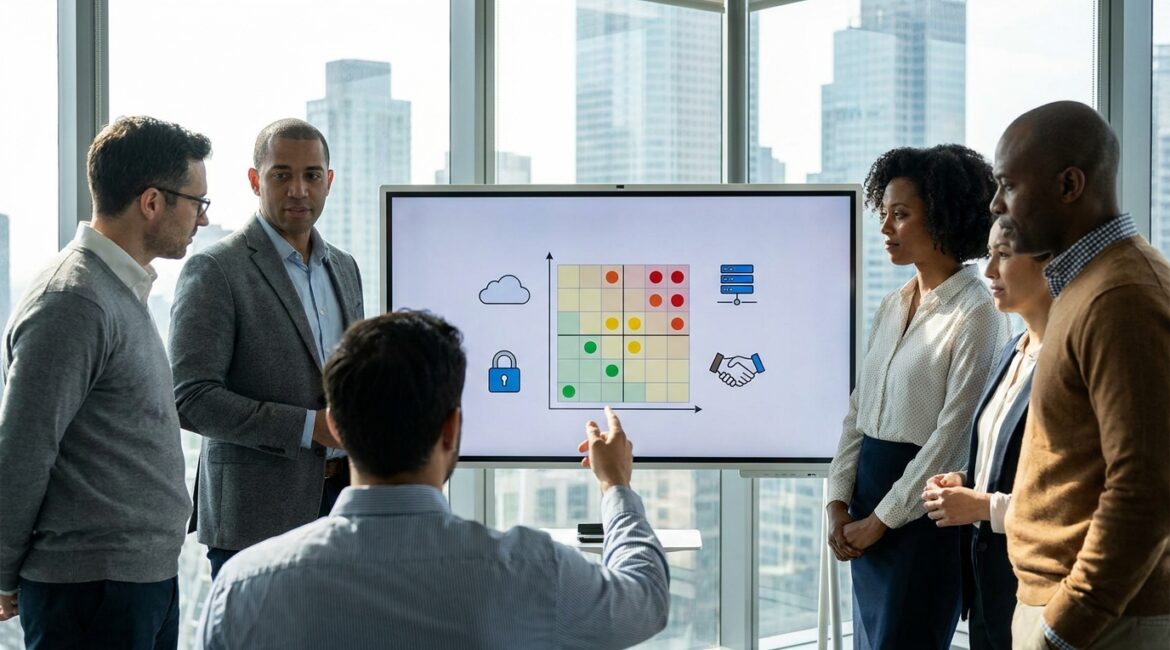
To identify and prioritize IT risks in your business, start by mapping critical business processes to the systems, data, and vendors that support them, then score each risk by likelihood and impact. Focus first on risks that could stop revenue, disrupt operations, or trigger regulatory exposure, and turn the results...
What Makes a Great IT Partner vs a Basic IT Provider?
A great IT partner does more than fix tickets and maintain devices. They align technology with your business goals, reduce risk, and take shared accountability for outcomes, not just activity. A basic IT provider may keep systems running, but rarely delivers proactive strategy, measurable security improvement, or long-term planning. Why...