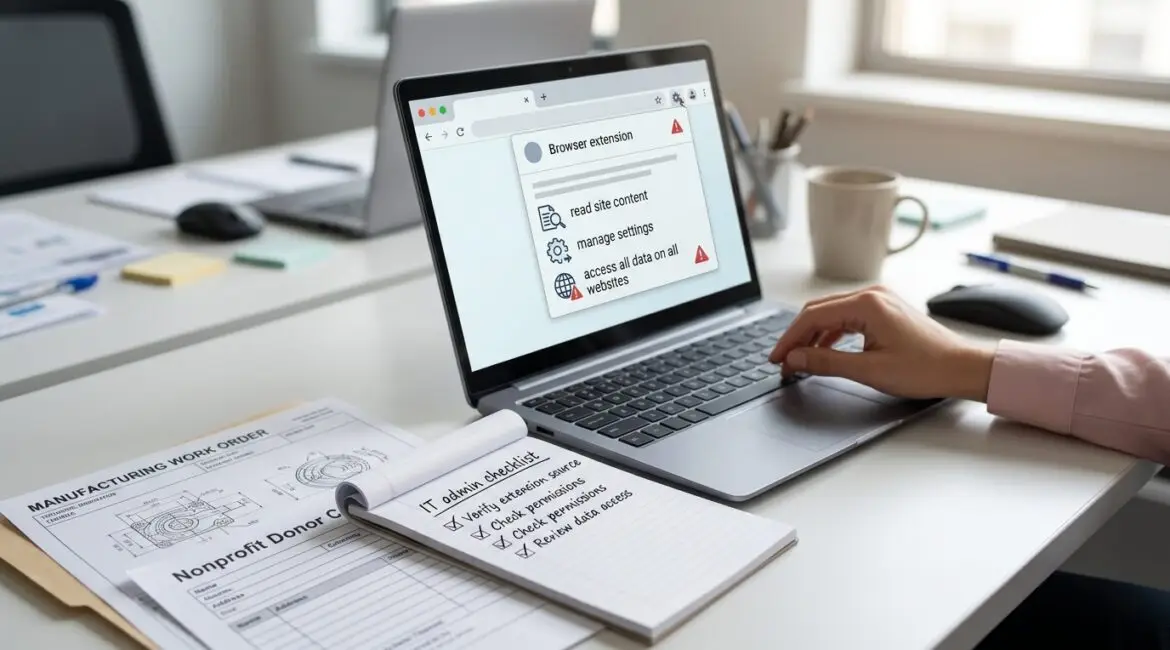
To protect your business from malicious browser extensions, limit which extensions employees can install, standardize approved browsers, monitor for unauthorized add-ons, and train staff to treat extensions like software, not harmless shortcuts. A single bad extension can capture passwords, read email, copy customer data, or redirect users to fraudulent websites without much warning.
For many businesses, the browser has become a primary work tool. Your team uses it for Microsoft 365, banking portals, CRM systems, donor platforms, document sharing, payroll, and vendor access. That makes browser extensions a business risk, not just a personal device issue.
Why browser extensions are risky for businesses
A browser extension is a small add-on that changes how a web browser works. Some are useful. They can help with password management, grammar checking, screen capture, or productivity tasks. The problem is that extensions often request broad access to browsing activity, page contents, downloads, and stored credentials.
If that access falls into the wrong hands, the extension can become a quiet data collection tool inside your business. Unlike obvious malware, a malicious extension may look legitimate, work as expected, and still siphon information in the background.
Common business risks include:
- Credential theft from login pages for email, accounting, and cloud applications
- Data exposure when extensions read client records, donor data, legal documents, or financial details displayed in the browser
- Session hijacking through stolen browser cookies or tokens
- Phishing assistance by redirecting users to fake websites or altering search results
- Productivity loss from browser crashes, pop-ups, slow performance, or support calls
This is especially relevant for manufacturers, nonprofit organizations, and professional service firms. A manufacturer in Southeast Wisconsin might have staff accessing supplier portals, shipping systems, and ERP dashboards all day. A nonprofit in Kenosha may use web-based fundraising and volunteer management tools. A law office or accounting firm in Northeast Illinois may live inside browser-based document and client systems. In each case, one unsafe extension can touch sensitive information quickly.
How malicious browser extensions get into the workplace
Most bad extensions do not arrive through a dramatic cyberattack. They usually enter through normal employee behavior.
Employees install them for convenience
A team member wants a PDF helper, coupon finder, AI note taker, screenshot tool, or calendar widget. It takes seconds to install, and the request for permissions is often ignored.
Legitimate extensions get sold or compromised
Sometimes an extension starts out safe. Later, the developer sells it, stops maintaining it, or pushes an update that changes what it does. That means an extension approved a year ago may not be safe today.
Fake listings imitate trusted tools
Attackers create lookalike extensions that mimic popular brands. An employee searching quickly may install the wrong one, especially if the name and icon appear familiar.
No one owns browser governance
Many organizations manage laptops, antivirus, and Microsoft 365 carefully but have no policy for browser extensions. That gap creates the same kind of inconsistency discussed in configuration drift, where settings slowly move away from an approved standard.
What a malicious extension can cost your business
The damage is not always immediate, but it adds up fast. If one employee in finance installs a harmful extension and it captures Microsoft 365 session data, an attacker may gain access to email, invoices, and file storage. That can lead to fraudulent payment requests, data review work, password resets, and incident response costs.
Even a smaller event can be expensive. If 15 employees lose two hours each while IT investigates browser pop-ups, removes extensions, resets accounts, and restores settings, that is 30 hours of lost productivity. At an average loaded labor cost of $40 per hour, that is $1,200 in internal time before outside support or business disruption is counted.
For nonprofits and regulated firms, there may also be reputational and compliance concerns. If donor records, client communications, or financial information are exposed through a browser session, the follow-up work can easily outweigh the original technical problem.
Practical ways to reduce the risk
1. Create an approved extension list
Treat browser extensions like business software. Decide which ones are allowed, who approves them, and which departments truly need them. Most organizations need far fewer extensions than employees install on their own.
For example, you may approve:
- A company-managed password manager extension
- A secure PDF signing tool
- A sanctioned screen capture utility
Everything else should require review.
2. Restrict local admin rights and browser settings
If employees can install anything they want, risk rises quickly. Limiting administrative rights and using centralized browser policies can stop unauthorized extensions before they spread.
This is one reason browser security should be part of a broader management plan. Platinum Systems often helps businesses standardize these controls so the browser is governed like any other business application.
3. Standardize on supported browsers
When every employee uses a different browser with different settings, support becomes harder and risk becomes less visible. Standardizing on one or two approved browsers makes extension control, patching, and troubleshooting much easier.
If your environment has grown messy over time, our article on how to build an IT environment that is easier to manage explains why standardization reduces both cost and security issues.
4. Review extension permissions carefully
Some permissions should raise immediate questions. Be cautious if an extension asks to:
- Read and change data on all websites
- Access browser tabs and browsing history
- Manage downloads
- Read clipboard contents
- Access cookies or session data
If the business purpose is minor but the permissions are broad, it is probably not worth the risk.
5. Monitor for unauthorized extensions
You cannot manage what you cannot see. Inventory approved browsers and installed extensions across company devices. This fits well with broader visibility work, including knowing what software and services are actually in use.
Businesses that already struggle with unapproved apps should also review how to reduce software sprawl across your organization. Extensions are often part of the same problem.
6. Include extensions in security awareness training
Most employees understand suspicious email links better than suspicious browser add-ons. Training should explain that extensions can read what is on the screen, collect data, and affect logins. Staff should know not to install tools just because they appear in an official browser store.
7. Use layered protection
No single control is enough. Strong identity security, endpoint protection, DNS filtering, browser policy management, and logging all help reduce the impact if something slips through. If an extension tries to connect to known harmful domains, tools like secure DNS may help block that traffic.
Warning signs your business may already have an extension problem
You do not need a confirmed security incident to justify a review. Common signs include:
- Browsers running unusually slow or crashing often
- Unexpected ads, redirects, or changed search behavior
- Employees reporting repeated login prompts
- Unauthorized SaaS sign-ins or strange account activity
- Different browser behavior from one user to another on the same systems
- IT not knowing which extensions are installed company-wide
These symptoms do not always mean malicious activity, but they do suggest the browser environment is not under enough control.
Make browser extension security part of technology governance
The bigger issue is not one bad extension. It is the absence of a decision-making process around everyday technology risk. Browser extensions are a good example of why governance matters. Small, convenient tools can create outsized business exposure when nobody owns approval, monitoring, and policy enforcement.
That is why proactive planning matters more than emergency cleanup. A simple review of browser standards, approved extensions, identity controls, and endpoint policies can prevent avoidable incidents and reduce support time later.
Final thoughts
Malicious browser extensions are easy to overlook because they often look helpful, familiar, and low risk. For businesses, they should be treated as software with access to sensitive systems and data.
If you are ready to strengthen your technology, reduce risk, and plan for the future, contact Platinum Systems to schedule a technology strategy discussion. We can help you evaluate browser controls, user access, and broader security standards so your environment is easier to manage and safer to operate.