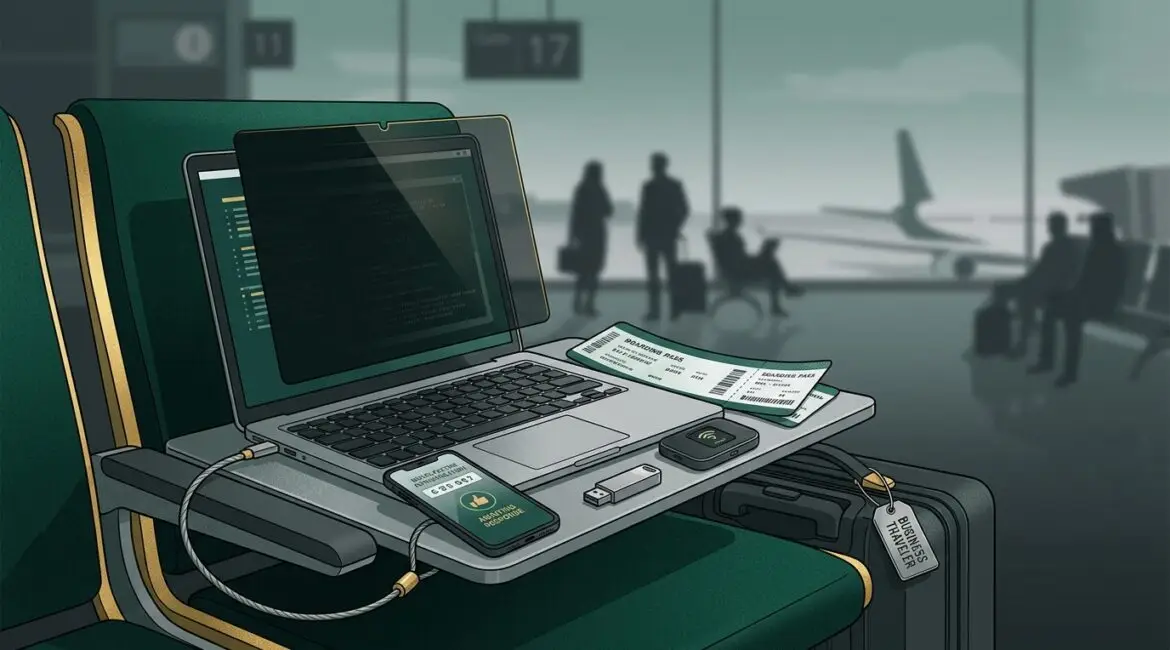
To reduce security risk when employees travel for business, start before the trip. Give employees company-managed devices, require multi-factor authentication, limit what data travels with them, and set clear rules for Wi-Fi, charging, file sharing, and lost devices.
Business travel creates a different kind of exposure than office work. People log in from hotels, airports, client sites, and mobile hotspots. Devices get left in rideshares, phones connect to unknown chargers, and rushed employees are more likely to click the wrong link or bypass a security step to keep work moving.
Why business travel creates extra risk
When employees work from the office, your business has more control. The network is known, devices are easier to monitor, and support is close by. Travel removes much of that control.
That does not mean employees should stop traveling. It means your business should plan for the predictable risks that come with it.
- Public networks can expose traffic or make it easier for attackers to trick users.
- Lost or stolen devices can put email, files, saved passwords, and client data at risk.
- Shoulder surfing happens when someone nearby sees sensitive information on a screen.
- Phishing and fake login pages often work better on the road because employees are distracted.
- Unapproved apps and workarounds increase when people need to move quickly.
A manufacturer sending sales staff to trade shows, a nonprofit leader traveling to donor meetings, or a law firm partner working between client visits all face the same basic problem. The employee still needs access to business systems, but the environment around them is less trustworthy.
Start with the device, not the destination
The safest travel plan begins with a properly managed device. If an employee travels with an old personal laptop or an unmanaged tablet, your risk goes up immediately.
Company travel devices should be current, encrypted, patched, and monitored. They should also follow a replacement schedule so older hardware does not become the weak point. If your organization has not formalized that process, device lifecycle planning is worth addressing before travel season gets busy.
Minimum device standards for traveling employees
- Full disk encryption so stolen devices do not expose stored data
- Automatic screen lock after a short period of inactivity
- Endpoint protection with centralized monitoring
- Current operating system and application updates
- Remote lock and wipe capability
- Standard browser and approved business apps only
This is especially important for organizations in Southeast Wisconsin and Northeast Illinois that have lean internal IT resources. Standardization makes it easier to support travelers quickly when something goes wrong in Chicago, Milwaukee, Kenosha, or across the country.
Use stronger sign-ins and reduce password exposure
Travel increases the chance that a password is stolen, reused, or entered into the wrong page. Strong identity controls help contain that risk.
At minimum, require multi-factor authentication for email, cloud applications, VPN access, and any remote administrative tools. If employees still rely heavily on passwords alone, travel is a good reason to improve that model.
Practical identity controls that matter on the road
- Multi-factor authentication for every critical system
- Password managers instead of passwords stored in browsers or spreadsheets
- Conditional access rules that flag unusual sign-in behavior
- Short session timeouts for sensitive applications
- Disabled local admin rights for most users
For example, if a consulting employee logs into Microsoft 365 from Wisconsin in the morning and another country an hour later, your system should challenge or block that access. Tools like Microsoft Entra ID can help businesses apply those controls in a practical way without making travel unworkable.
Limit the data that travels
One of the simplest ways to reduce exposure is to avoid carrying unnecessary data in the first place. Many businesses still let employees download large folders to laptops just in case they need them. That creates avoidable risk.
Instead, decide what must be available offline and what should stay in secured cloud systems. Sensitive files such as donor records, financial reports, legal documents, or customer pricing should be handled according to their importance. If your team has never defined that clearly, data classification is a useful next step.
Examples of smarter travel data handling
- A nonprofit executive traveling to a fundraising event may only need presentation materials and a limited donor contact list, not the full donor database.
- A manufacturer visiting distributors may need product sheets and approved pricing, not broad access to internal engineering files.
- An accounting or legal professional may need secure portal access rather than local copies of client records.
If a laptop is stolen from a rental car, the difference between a few protected files and years of business records is significant.
Train employees for the situations they will actually face
Good travel security training should be short, specific, and realistic. Employees do not need a long technical lecture before boarding a flight. They need clear instructions for common decisions.
Cover these travel scenarios in plain language
- Wi-Fi: Use approved connections only. Avoid open public Wi-Fi when possible. Use a company-approved VPN or secure mobile hotspot if required by your policy.
- Charging: Use personal charging adapters and battery packs instead of unknown public USB ports.
- Screens: Do not review payroll, legal, donor, or client data where others can easily see it.
- Calls: Be careful discussing contracts, personnel issues, or financial details in public places.
- Links and attachments: Slow down before signing in through email prompts, especially while traveling.
- Physical security: Keep devices with you, not checked in luggage.
A 15-minute pre-travel checklist often does more good than an annual one-hour training session. The key is making secure behavior easy to remember during a busy trip.
Prepare for lost devices and urgent support issues
Even well-prepared employees lose phones and laptops. What matters is how quickly your business can respond.
If a traveling employee reports a missing device at 8:30 p.m., your team should already know what happens next. Who disables the account? Who checks recent sign-ins? Can the device be locked or wiped? How does the employee keep working the next morning?
Your travel incident response plan should include
- A single number or email for urgent reporting
- Steps for disabling accounts and sessions quickly
- Remote wipe or lock procedures
- Backup device or loaner options for frequent travelers
- Documentation of critical apps and recovery steps
The business cost of delay adds up quickly. If a salesperson loses a laptop before a client presentation, one missed meeting could cost far more than the device itself. If an executive cannot access email and files for half a day, the productivity loss can affect scheduling, approvals, and customer communication across the team.
Do not let convenience create shadow IT on the road
Travel often pushes employees toward quick fixes. They forward files to personal email, install a random scanning app, or use a consumer file-sharing tool because it seems faster in the moment.
Those habits create long-term support and security problems. Businesses reduce that risk by giving employees approved tools that are easy to use before they leave. Secure file access, secure collaboration, and encrypted email should be part of the plan, not an afterthought.
If your organization regularly shares sensitive information while people are away from the office, it may also be time to review whether secure email encryption should play a larger role.
Build travel security into your broader technology plan
Travel security works best when it is tied to larger business decisions. It connects to device standards, identity management, acceptable use policies, support procedures, and budgeting.
That is why proactive planning matters. A business that reviews travel risk once a year, updates policies before major events, and budgets for secure devices will usually spend less than a business that responds after a lost laptop, compromised account, or emergency support call.
For many organizations, especially growing firms across Kenosha, Southeast Wisconsin, and Northeast Illinois, travel security is one part of a larger need for better governance and planning. It should not depend on whether a frequent traveler happens to be tech-savvy.
A practical travel security checklist for business leaders
- Issue managed, encrypted devices for travel
- Require multi-factor authentication on business accounts
- Limit locally stored sensitive data
- Provide approved tools for file sharing and communication
- Train employees on Wi-Fi, charging, screen privacy, and phishing
- Set clear lost device reporting steps
- Review travel security policies before busy travel periods
- Test remote lock, wipe, and account recovery procedures
Most of these steps are not expensive compared with the cost of an incident. A privacy screen, password manager, mobile hotspot, or replacement laptop budget is minor next to the downtime, legal review, reputational damage, or client disruption that can follow a preventable mistake.
Conclusion
Reducing travel-related security risk is mostly about preparation, consistency, and clear expectations. When employees have the right devices, the right access controls, and simple guidance for real-world situations, business travel becomes much easier to manage safely.
If you’re ready to strengthen your technology, reduce risk, and plan for the future, contact Platinum Systems to schedule a technology strategy discussion.