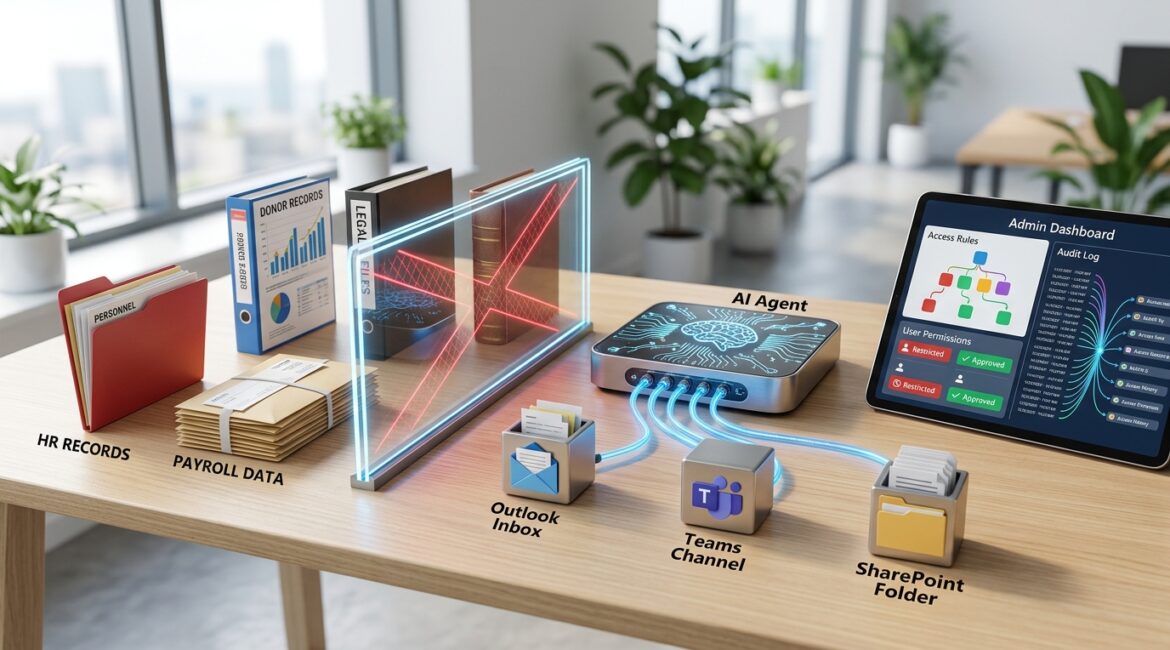
Yes, AI agents can work with Microsoft 365 without exposing sensitive data, but only if access is tightly controlled from the start. The safest approach is to treat an AI agent like a new employee or outside contractor: give it only the information it needs, restrict where it can go, and monitor what it does.
That matters because Microsoft 365 often holds your email, files, Teams chats, calendars, contracts, donor records, financial documents, and internal discussions. If an AI tool is connected carelessly, it can surface information to the wrong person, pull from the wrong location, or create compliance problems your team did not expect.
Why this question matters for business leaders
Many businesses are interested in AI for simple reasons. They want faster reporting, better meeting summaries, quicker document drafting, and less administrative work. Those are reasonable goals.
The concern is that Microsoft 365 is rarely a clean, perfectly organized environment. In many companies across Southeast Wisconsin and Northeast Illinois, years of growth have created a mix of shared mailboxes, old SharePoint folders, broad permissions, and files that were never labeled by sensitivity.
If you connect an AI agent to that environment without preparation, the agent may not break security controls. It may simply follow the access rules that already exist. If those rules are too open, the risk comes from your setup, not the AI itself.
What an AI agent actually does inside Microsoft 365
In plain English, an AI agent is software that can read information, respond to prompts, and sometimes take approved actions. Inside Microsoft 365, that may include reviewing emails, summarizing Teams conversations, finding documents, drafting responses, scheduling tasks, or pulling data into reports.
For example, a professional services firm might want an AI assistant to summarize client meeting notes from Teams and create follow-up tasks. A manufacturer might want an agent to pull production meeting action items from email and post them into a shared planning channel. A nonprofit might want help drafting grant updates based on approved documents stored in SharePoint.
Those uses can save time. But they also show why access boundaries matter. If the AI can see everything, it may summarize more than it should.
The biggest data exposure risks to watch for
Overly broad permissions
This is the most common issue. If employees already have access to large file libraries or shared mailboxes they do not really need, an AI agent working on their behalf may be able to pull that same information into answers or drafts.
Unlabeled sensitive data
If your business has not identified what is confidential, private, regulated, or public, the AI has no business context to follow. Payroll reports, donor lists, HR records, legal files, and board materials should not be treated the same as a general policy document.
Shadow workflows
Teams sometimes connect tools without formal review. That can happen when a department signs up for an AI add-on using a company Microsoft 365 account but without IT or leadership evaluating the data impact first.
Accidental oversharing in collaboration tools
Microsoft Teams, SharePoint, and OneDrive make collaboration easy, but they also make it easy to share too broadly. If a folder was opened to an entire department years ago for convenience, an AI tool may inherit that access path.
How to let AI agents use Microsoft 365 safely
You do not need a perfect environment before using AI. You do need a controlled one. Start with these practical steps.
1. Limit access by role, not convenience
AI agents should only access the data needed for a specific business purpose. If the goal is meeting summaries for the operations team, the agent does not need HR files, executive mailboxes, or finance folders.
This is where identity and access controls matter. If your Microsoft 365 permissions are messy, fix that before expanding automation. Our article on Microsoft Entra ID security controls explains how stronger identity management supports safer access decisions.
2. Classify sensitive information
Not every file deserves the same treatment. Businesses should define categories such as:
- Public
- Internal use only
- Confidential
- Highly sensitive or regulated
Once data is classified, you can apply different rules for sharing, retention, and AI access. This is especially useful for nonprofits handling donor information, CPA firms managing tax records, and manufacturers protecting pricing, vendor contracts, or product documentation. If your organization has not done this work yet, data classification is a strong place to start.
3. Separate pilot projects from the whole environment
Do not connect an AI agent to everything on day one. Start with a small use case, a defined user group, and a limited data set. For example, a Kenosha-based nonprofit might pilot AI-generated board meeting summaries using only a specific Teams site and a small document library.
This reduces risk and gives leadership a clearer view of value. If the pilot saves five managers 30 minutes a day, that is meaningful. At an average loaded labor cost of $40 to $60 per hour, that can add up to $1,000 or more in monthly productivity gains without exposing your entire tenant.
4. Use approval steps for higher-risk actions
Reading and summarizing information is one level of risk. Sending messages, changing files, or triggering workflows is another. Higher-risk actions should require human approval.
For instance, an AI agent can draft a vendor response or prepare a policy summary, but a person should review it before it is sent externally or stored as an official record.
5. Monitor activity and review logs
You should be able to answer basic questions such as:
- What data sources can the agent access?
- Who approved those permissions?
- What actions has it taken?
- Were any unusual data requests made?
Visibility matters here. If you cannot see what is happening, you cannot manage risk well. That is one reason businesses benefit from regular Microsoft 365 reviews and tools like Security Score monitoring.
6. Build AI use into technology governance
AI should not be treated as a side experiment. It belongs in your broader technology governance process, alongside access control, vendor review, acceptable use, and data protection. Businesses that plan this well avoid the expensive pattern of adopting tools first and cleaning up the mess later.
If your leadership team is already working on budgeting and long-term planning, this is a good time to include AI use cases in your broader annual IT planning calendar.
What safe AI use looks like in real organizations
Manufacturer example
A 75-person manufacturer wants AI help with production meeting recaps and maintenance coordination. The safe approach is to limit the agent to specific Teams channels, approved SharePoint libraries, and a defined group of supervisors. It should not have access to HR records, acquisition plans, or finance documents.
Nonprofit example
A regional nonprofit wants AI to draft donor acknowledgment letters and summarize grant program notes. The right design would separate donor databases, board records, and program documentation so the agent only works from approved content. That protects donor privacy and reduces the chance of mixing confidential fundraising details into the wrong output.
Professional services example
An accounting or legal support firm may want AI to organize internal notes and produce first-draft summaries. In that case, matter-level or client-level access boundaries are essential. One client’s information should never be visible in another client’s workflow.
Common mistakes that create unnecessary risk
- Granting broad access because it is faster than cleaning up permissions
- Using shared accounts instead of individual identities
- Skipping data classification
- Allowing departments to adopt AI tools without review
- Failing to document what the agent can access and do
- Assuming Microsoft 365 defaults match your business risk tolerance
These are management issues as much as technical ones. In most cases, the problem is not the AI feature. It is the lack of structure around it.
What business leaders should ask before approving AI in Microsoft 365
- What exact problem are we trying to solve?
- What data will the AI need to access?
- Is that data already organized and permissioned correctly?
- What information must be excluded?
- Who is accountable for reviewing access and results?
- How will we measure productivity gains against risk and cost?
Those questions help turn AI from a novelty into a business tool with clear boundaries.
Conclusion
AI agents can work safely with Microsoft 365, but only when businesses control access, classify sensitive data, start with limited use cases, and monitor activity over time. The real goal is not to connect AI to everything. It is to use automation where it improves operations without creating unnecessary exposure.
If you’re ready to strengthen your technology, reduce risk, and plan for the future, contact Platinum Systems to schedule a technology strategy discussion.