Privileged identity management is the practice of tightly controlling who gets elevated access to critical systems, when they get it, and what they can do with it. Businesses should use it when they have administrator accounts, sensitive cloud systems, outside vendors, compliance obligations, or simply want to reduce the risk of one powerful account causing a major security or operational problem.
In plain English, it keeps the keys to your most important technology from being shared too freely or left available all the time.
What privileged identity management means in plain English
Every business has some accounts with far more power than a normal employee login. These are often called privileged accounts. They may be able to reset passwords, change security settings, install software, access financial systems, manage servers, or control Microsoft 365 and other cloud platforms.
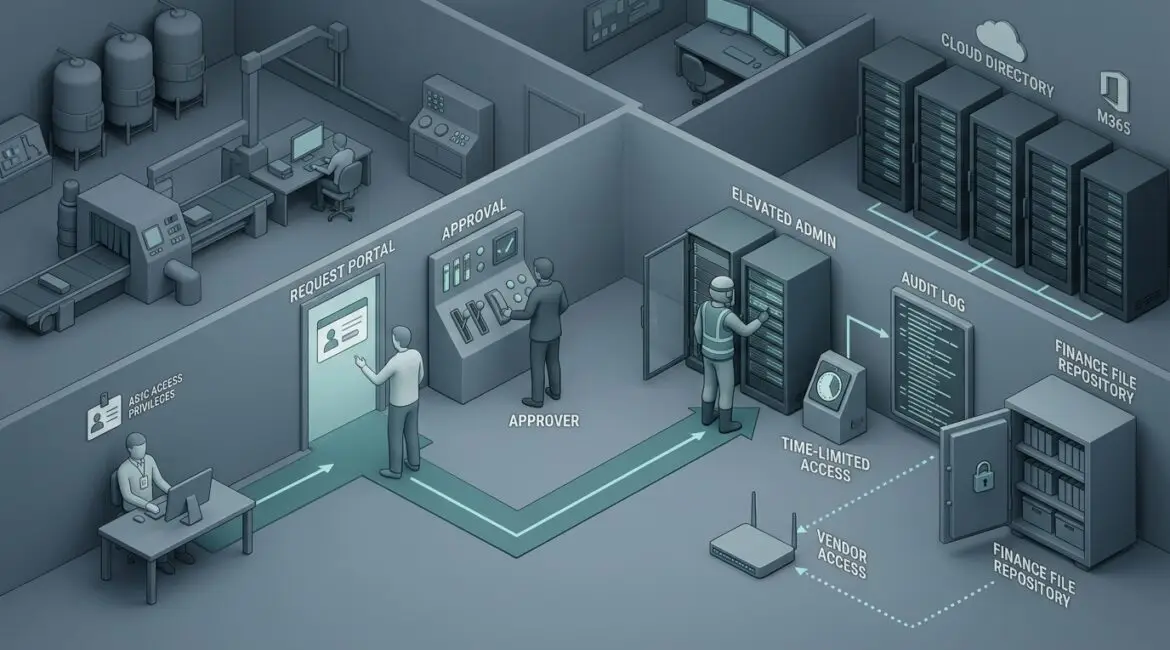
Privileged identity management puts extra rules around those accounts. Instead of giving permanent admin rights to anyone who might need them once in a while, the business can limit access, approve it when needed, and keep records of what happened.
Think of it like a controlled key cabinet in a manufacturing plant. Not everyone gets a master key in their pocket. The right person can check one out for a specific task, for a limited time, and there is a record showing who used it.
Why these accounts deserve special attention
If a standard user account is compromised, the damage may be limited to one mailbox or one device. If an administrator account is compromised, the impact can spread quickly across the business.
A single privileged account can be used to:
- Disable security tools
- Create new user accounts
- Access confidential files
- Change backup settings
- Alter email rules
- Install malicious software
- Lock legitimate users out of systems
That is why privileged access is a business issue, not just an IT issue. One mistake or one stolen admin login can lead to downtime, lost billable hours, recovery costs, and difficult conversations with clients, donors, or auditors.
How privileged identity management works
The exact tools vary, but the core idea is consistent. High-level access is restricted, approved, time-limited, and monitored.
Common controls include
- Just-in-time access: admin rights are granted only when needed, not left on permanently
- Approval workflows: a manager or IT lead approves elevated access requests
- Role-based access: people get only the level of access required for their job
- Multi-factor authentication: privileged users must verify their identity with more than a password
- Session logging: activity performed with elevated rights is recorded for review
- Privileged account separation: users have one normal account for daily work and a separate admin account for higher-risk tasks
- Automatic expiration: privileged access ends after a set period unless renewed
These controls reduce the chance that admin rights are misused, forgotten, or quietly exploited.
When a business should start using privileged identity management
Not every organization needs an enterprise-scale program on day one. But many small and midsize businesses reach the point where basic admin account habits are no longer enough.
You should consider it if your business has
- More than one person with administrator access
- Microsoft 365, Azure, or other cloud platforms with sensitive settings
- Outside IT vendors or software partners that need elevated access
- Regulatory, insurance, legal, or client security requirements
- Shared admin passwords or undocumented service accounts
- Remote administration across multiple locations
- Frequent employee turnover in finance, operations, or IT roles
For many organizations in Southeast Wisconsin and Northeast Illinois, this becomes relevant earlier than expected. A growing manufacturer in Kenosha may have plant systems, ERP access, Microsoft 365 administration, and remote vendor support all at once. That creates several privileged access paths, even if the company does not think of itself as complex.
Business examples that make the need clear
Manufacturer with vendor access
A manufacturer may rely on an outside vendor to maintain production software or shop floor equipment. If that vendor has standing admin access 24 hours a day, the account becomes a permanent risk. Privileged identity management can limit that access to approved maintenance windows and record what changes were made.
That matters when an unexpected change stops label printing, inventory syncing, or machine communication. Even two hours of production delay can cost far more than the security control that would have reduced the risk.
Nonprofit with lean staffing
A nonprofit often has a small internal team, shared responsibilities, and tight budgets. It may also handle donor records, payroll, grant documentation, and board communications. If one operations leader has broad access to everything all the time, the organization may be one phishing email away from a serious disruption.
With privileged identity management, elevated access can be limited to specific tasks and protected with stronger sign-in controls. That helps reduce risk without requiring a large internal IT department.
Professional services firm with client confidentiality obligations
An accounting firm, law office, or engineering firm may have staff who occasionally need admin rights to manage document systems, email permissions, or line-of-business applications. Permanent admin access increases the chance of accidental changes, data exposure, or unauthorized software installation.
Time-based elevation is often a better fit. Staff can do the work they need to do, but the access does not stay open longer than necessary.
What problems it helps prevent
Privileged identity management is not only about stopping attackers. It also helps prevent internal mistakes and support problems.
- Accidental misconfiguration: a user with too much access changes a setting that disrupts email, backups, or file permissions
- Shared credential confusion: multiple people use the same admin account and no one knows who changed what
- Lingering access: former employees, contractors, or vendors keep privileges after they no longer need them
- Audit gaps: the business cannot show who had elevated access during a key event
- Security tool bypass: malware or a bad actor uses admin rights to disable protections
This is closely tied to broader access control and governance. Businesses that are already reviewing account structure may also benefit from reading data classification and technology governance to make sure access decisions align with business priorities.
What it can save in real business terms
Leaders often ask whether this is worth the effort. In many cases, yes.
Consider a 40-person professional services firm where five employees have full admin rights all the time. One compromised account leads to a Microsoft 365 disruption that locks staff out for half a day. If average loaded labor cost is $45 per hour, four hours of lost productivity across 40 employees is about $7,200, before client delays, recovery work, or reputational impact.
Now compare that with the cost of planning and implementing tighter privileged access controls as part of a broader identity strategy. The financial case becomes easier to understand.
How to know if your current setup is too loose
Watch for these warning signs
- Employees use one account for both normal work and administration
- Admin passwords are stored in spreadsheets or shared notes
- No one reviews privileged accounts on a regular schedule
- Vendors have open-ended remote access
- Former staff accounts are disabled, but service or admin accounts remain untouched
- There is no clear approval process for elevated access
If several of these sound familiar, the issue is probably not the lack of one product. It is the lack of a structured access strategy. Articles like secure vendor access and using Microsoft Entra ID to improve business security can help frame the next steps.
How businesses should approach it without overcomplicating things
The goal is not to make every admin task slow or frustrating. The goal is to give elevated access structure.
A practical starting point looks like this
- Identify every privileged account, including vendor and service accounts
- Separate normal user accounts from admin accounts
- Require multi-factor authentication for all privileged access
- Remove standing admin rights where they are not truly necessary
- Set approval and expiration rules for elevated access
- Review privileged accounts on a recurring schedule
- Document ownership and business purpose for each account
This works best when it is part of proactive planning, not a rushed response after an incident. A periodic review can also fit naturally into an IT health check or annual planning cycle.
Conclusion
Privileged identity management helps businesses control the accounts that can do the most damage if misused, whether by mistake or by compromise. If your organization depends on cloud platforms, outside vendors, sensitive data, or a small number of people with broad access, it is worth reviewing how those privileges are granted and monitored.
If you’re ready to strengthen your technology, reduce risk, and plan for the future, contact Platinum Systems to schedule a technology strategy discussion.