If your business has no internal IT staff, the best way to create an IT strategy is to start with business priorities, identify your biggest technology risks, document what you already have, and assign clear outside ownership for support, security, and planning. A good strategy does not need to be complicated. It needs to help you make better decisions before problems become expensive.
Many small and midsize organizations run this way. A manufacturer in Southeast Wisconsin may have one operations manager handling vendors. A nonprofit in Kenosha may rely on an office administrator who is already wearing five hats. A law firm or accounting practice in Northeast Illinois may depend on a mix of software vendors and whoever knows the most about printers and passwords. That can work for a while, but without a plan, technology decisions become reactive, inconsistent, and costly.
Start with business goals, not hardware
Your IT strategy should support how the business operates. Before talking about devices, cloud tools, or cybersecurity products, define what the business needs technology to do over the next 12 to 36 months.
- Growth: Are you adding staff, opening a location, or expanding services?
- Reliability: What systems cannot be down during the workday?
- Security: What data would cause serious problems if exposed or lost?
- Compliance: Do you handle donor records, financial data, legal files, or client confidential information?
- Budget control: Do you need predictable monthly spending instead of surprise replacement costs?
For example, if a 25-person professional services firm loses access to email and files for half a day, that may mean missed client deadlines, delayed billing, and 100 or more lost work hours. If a small manufacturer cannot print labels or access inventory systems for even two hours, production may slow or stop. Those are business problems first, and technology problems second.
Build a clear picture of your current environment
You cannot plan well if you do not know what you own, who supports it, or when it should be replaced. This is where many businesses without IT staff struggle. They have devices, software subscriptions, internet service, backups, and vendor relationships, but no single source of truth.
Start by documenting:
- Computers, laptops, servers, and network equipment
- Business applications and subscriptions
- Email and file storage platforms
- Internet providers and phone systems
- Backup systems
- Cybersecurity tools
- Admin accounts and password ownership
- Outside vendors and support contacts
- Warranty and replacement dates
If that sounds basic, it is. It is also essential. Without this information, simple changes take longer, support costs rise, and security gaps stay hidden. A good starting point is a structured inventory and health review. Our article on what an IT health check should include explains what to look for.
Identify the systems that matter most
Not every system deserves the same level of attention. Your IT strategy should focus first on the tools that keep revenue, operations, and client service moving.
Typical critical systems include:
- Email and calendars
- File storage and document access
- Line-of-business software
- Internet and network connectivity
- Phones and communications
- Backup and recovery tools
- Identity and login systems
Ask a simple question for each one: what happens if this is unavailable for four hours, one day, or three days?
A nonprofit may decide donor management and accounting systems are most critical during year-end giving season. A CPA firm may prioritize secure file access and email during tax season. A manufacturer may place internet connectivity, ERP access, and shop floor devices at the top of the list. Once you know what matters most, you can spend smarter.
Set practical priorities in five areas
For most organizations without internal IT staff, a workable strategy covers five categories.
1. Support and ownership
Someone must be responsible for day-to-day support, vendor coordination, and escalations. If nobody owns that function, issues linger and decisions stall.
Define:
- Who employees contact for help
- Who approves technology purchases
- Who manages vendor relationships
- Who has administrative access
- Who reviews performance and risk each quarter
This does not require a full-time employee. It does require clear accountability.
2. Security basics
Businesses without IT staff are often missing simple protections because nobody had time to set them up properly. Start with the fundamentals:
- Multi-factor authentication for email and cloud apps
- Managed endpoint protection
- Patch management for devices and software
- Secure backups
- Role-based access so employees only have what they need
- Security awareness training
If your team uses Microsoft 365, access controls and identity management deserve special attention. Our post on using Microsoft Entra ID to improve business security covers a practical example.
3. Lifecycle and replacement planning
One of the biggest mistakes small organizations make is replacing technology only after it fails. That approach creates rush purchases, downtime, and uneven spending.
A better plan maps likely replacement windows for laptops, firewalls, switches, wireless equipment, and servers. If ten laptops are all six years old, you probably do not want all ten failing in the same budget year. A staged schedule is far easier to manage. Our article on creating an IT replacement schedule explains how to avoid that budget spike.
4. Backup and recovery
Many leaders assume backup is handled because files are in the cloud or because a vendor mentioned it once. That is risky. Your strategy should define what gets backed up, how often, where it is stored, and how recovery is tested.
Think in plain terms:
- If a file is deleted, how quickly can it be restored?
- If a laptop is stolen, what data is exposed?
- If Microsoft 365 data is corrupted, what is the recovery plan?
- If the office loses internet for a day, how will people work?
Recovery planning matters just as much as backup itself.
5. Budgeting and governance
An IT strategy should help leaders say yes to the right spending and no to waste. That means setting standards for approved software, defining who can buy technology, and reviewing costs regularly.
Without governance, software sprawl grows fast. One department signs up for one file-sharing tool, another starts using a different project app, and a third keeps sensitive data in personal accounts because it was convenient. The result is higher cost, weaker security, and more support headaches.
Create a simple 12-month roadmap
Your strategy should end with a short, practical roadmap. Not a 60-page document that nobody reads. A one-page or two-page plan is often enough if it includes the right actions, owners, timing, and rough budget ranges.
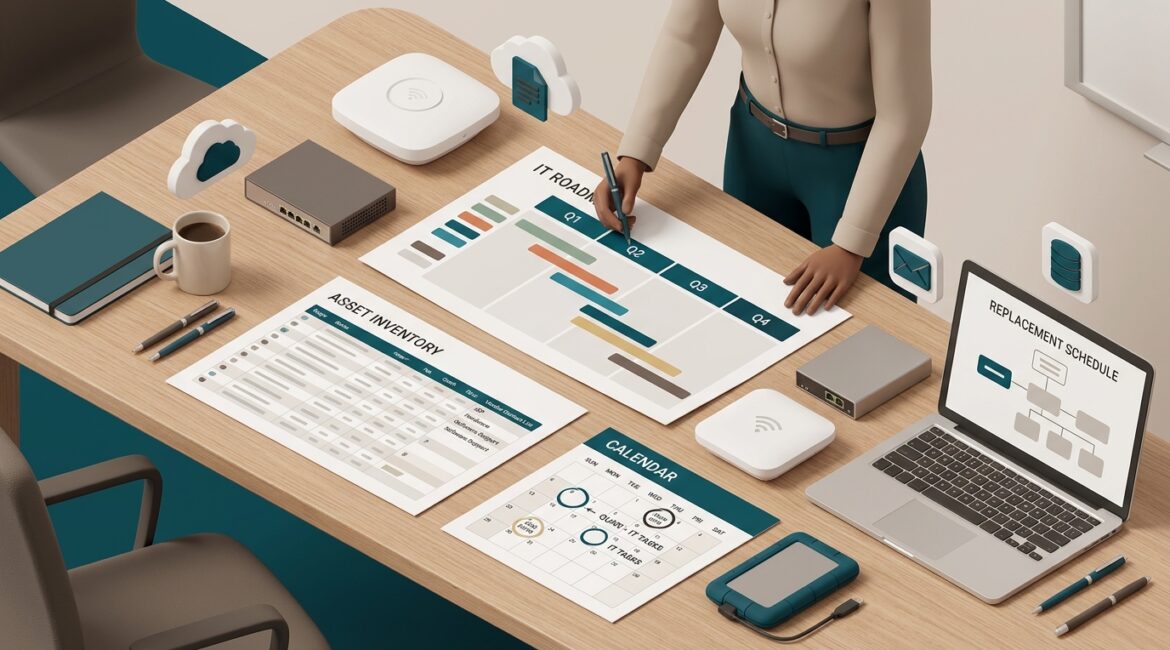
A sample 12-month roadmap might include:
- Quarter 1: inventory systems, review cybersecurity gaps, standardize support contacts
- Quarter 2: enable multi-factor authentication, clean up admin access, test backups
- Quarter 3: replace aging laptops, improve Wi-Fi reliability, document vendor accounts
- Quarter 4: review software subscriptions, plan next year budget, update recovery procedures
If you need a structure for scheduling these decisions, our post on building an annual IT planning calendar can help turn strategy into a repeatable process.
Know when outside guidance makes financial sense
For a business with no internal IT staff, outside guidance is often less expensive than staying reactive. Consider a 30-person firm where ten employees lose one hour each month to recurring login issues, slow devices, or file access problems. At an average loaded labor cost of $40 per hour, that is $4,800 per year in lost productivity, and that estimate is modest. It does not include downtime during outages, delayed client work, or emergency consulting fees.
The goal is not to outsource everything blindly. It is to make sure your business has access to planning, support, security oversight, and documentation at the level your operations require.
A trusted technology advisor can help you:
- Prioritize improvements based on business impact
- Avoid overspending on tools you do not need
- Reduce downtime through standardization and monitoring
- Strengthen cybersecurity without making daily work harder
- Build a realistic budget and replacement plan
What a good IT strategy looks like in real life
A good strategy is not flashy. It is organized, documented, and aligned with how your organization actually works.
For a nonprofit, that may mean protecting donor data, controlling software costs, and making sure staff can work during a temporary outage. For a manufacturer, it may mean reducing production interruptions and replacing aging network gear before it fails. For a law office or accounting firm, it may mean secure access, reliable email, and clear recovery steps during busy seasons.
In each case, the strategy should make technology easier to manage, less risky, and more predictable.
Conclusion
If your business has no internal IT staff, you do not need a perfect technology environment to build a smart IT strategy. You need a clear view of your systems, a realistic understanding of risk, defined ownership, and a practical plan for support, security, and replacement decisions.
If you’re ready to strengthen your technology, reduce risk, and plan for the future, contact Platinum Systems to schedule a technology strategy discussion. We help organizations across Southeast Wisconsin and Northeast Illinois make practical technology decisions that support long-term operations, not just short-term fixes.