A backup retention policy is a written rule that defines how long your business keeps backup copies of data before deleting or archiving them. How long you should keep data depends on your recovery goals, legal requirements, storage budget, and how far back you may need to restore after a mistake, outage, or cyber incident.
Many businesses have backups, but fewer have a clear retention policy. That gap causes problems. Some organizations keep too little and discover they cannot recover an older file, email, or database version when they need it. Others keep everything forever, which drives up cost, complicates recovery, and creates unnecessary risk.
What a backup retention policy actually does
Think of backups as time-stamped safety copies of your systems and files. A retention policy decides how many of those copies stay available and for how long.
For example, your business might keep:
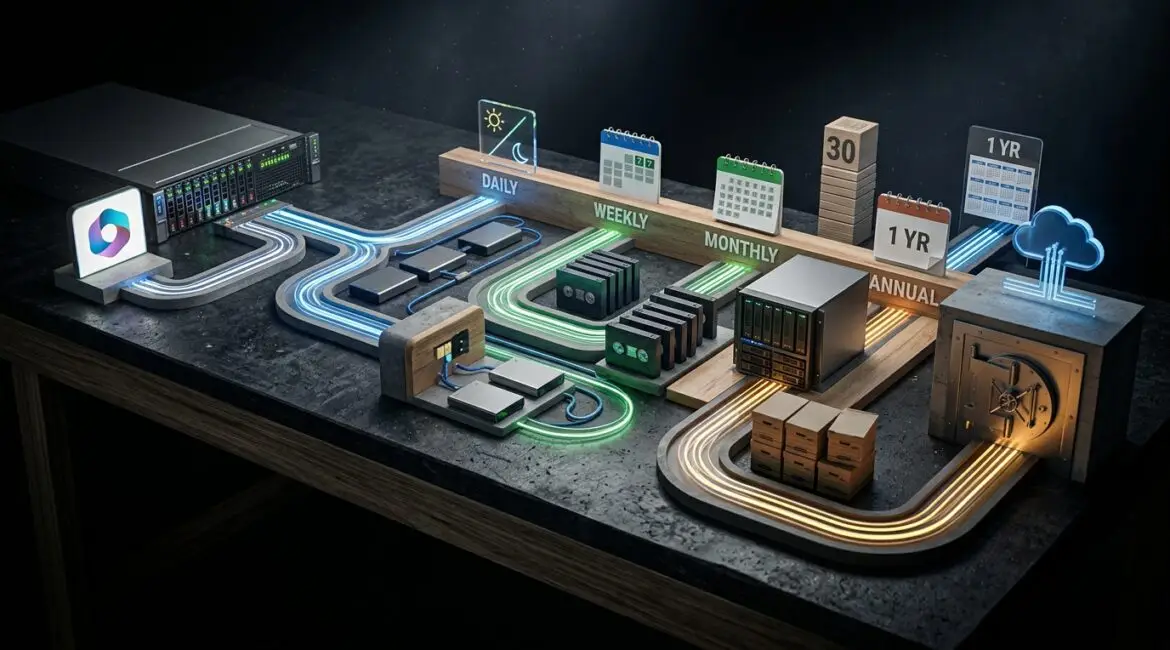
- Daily backups for 30 days
- Weekly backups for 12 weeks
- Monthly backups for 12 months
- Year-end backups for 7 years
That structure gives you recent restore points for everyday issues and older restore points for audits, disputes, or long-running problems that are discovered later.
This matters because not every recovery need looks the same. Restoring a file deleted yesterday is very different from recovering accounting records from last year or rebuilding systems after a ransomware event that went unnoticed for several weeks.
Why retention matters to business leaders
Retention is not just an IT setting. It is a business decision about risk, cost, and operational continuity.
If a manufacturer in Southeast Wisconsin loses production scheduling data and only has seven days of backups, that may not help if the issue started three weeks earlier. If a nonprofit in Kenosha needs donor communications from a prior campaign for reporting or legal review, short retention can create a real operational problem. If a law firm or accounting practice needs historical records for client matters, the wrong policy can lead to delays, rework, or compliance trouble.
There is also a cost side. Storing more backups for longer periods usually increases storage expense. But keeping too little can cost far more in downtime, lost billable time, missed deadlines, and manual reconstruction.
As a simple example, if a 20-person professional services firm loses access to a shared file set for half a day, the lost productivity alone can easily exceed the monthly cost difference between a minimal backup plan and a well-designed one.
How long should businesses keep backup data?
There is no single answer for every organization. A practical retention policy is based on a few key questions:
- How quickly do you need to recover?
- How far back might you need to restore?
- Do you have legal, contractual, or regulatory retention requirements?
- Which systems are most critical to operations?
- How much data changes every day?
- What is the cost of downtime compared with the cost of storage?
For many small and midsize businesses, a reasonable starting point looks like this:
- Daily backups: 14 to 30 days
- Weekly backups: 8 to 12 weeks
- Monthly backups: 6 to 12 months
- Annual backups: 1 to 7 years, depending on business and compliance needs
That is a starting point, not a rule. Some organizations need much longer retention for financial records, HR data, donor records, or client files. Others may need shorter periods for less critical systems.
Backup retention is not the same as file retention
This is where many businesses get confused. Backup retention and document retention are related, but they are not the same thing.
Backup retention
Backup retention is about recovery. It helps you restore systems, files, and data after deletion, corruption, hardware failure, or cyber incidents.
Document retention
Document retention is about keeping business records for legal, regulatory, operational, or historical reasons. Those records may belong in a document management system, secure archive, or line-of-business application, not just in backup storage.
Using backups as your long-term archive is usually inefficient and expensive. It also makes searches, legal holds, and record management harder than they need to be.
That is one reason data classification matters. If you have not defined which data is critical, sensitive, or long-term, it becomes much harder to set appropriate retention rules. Our article on data classification explains how that process supports better technology decisions.
Common mistakes businesses make
Keeping backups for too short a time
Short retention may save a little money, but it often fails during real incidents. Malware, accidental deletions, and data corruption are not always noticed right away.
If your team discovers a problem 21 days later and your backups only go back 14 days, recovery options may be limited or gone.
Keeping everything forever
Unlimited retention sounds safe, but it can create storage sprawl, higher bills, and more complexity. It may also preserve data longer than necessary, which can create legal or privacy concerns.
Using the same policy for every system
Your accounting platform, Microsoft 365 data, file server, and front desk workstation should not always be treated the same. Critical systems deserve more thoughtful retention planning than low-value or temporary data.
Never testing recovery from older backups
A policy on paper is not enough. You need to confirm that older backup points can actually be restored and that recovery times match business expectations.
This is closely tied to broader resilience planning. If you are reviewing backup strategy, it also helps to assess overall reliability and recovery readiness. Our post on improving the reliability of your business technology covers the bigger picture.
How to choose the right retention policy for your business
A good policy starts with business priorities, not backup software features.
1. Identify critical systems and data
List the systems that would seriously disrupt operations if they were unavailable or corrupted. For many organizations, that includes:
- Accounting and payroll systems
- Microsoft 365 email and files
- Line-of-business databases
- Shared file storage
- CRM and donor management platforms
- Production or scheduling systems
2. Match retention to business risk
Ask how far back you may need to go in a realistic incident. A simple file deletion might require yesterday’s backup. Fraud investigation, silent corruption, or ransomware may require a restore point from weeks or months earlier.
3. Review legal and contractual requirements
Different industries have different expectations. Professional service firms may need longer record availability. Nonprofits may need to preserve grant, donor, or board-related records. Manufacturers may need to retain quality, production, or customer documentation based on contracts or industry standards.
4. Separate archive needs from recovery needs
If a record needs to be kept for seven years, that does not automatically mean it belongs in a seven-year backup set. In many cases, it should be archived in a more appropriate system while backups focus on operational recovery.
5. Build the policy into your annual planning
Retention should be reviewed as part of budgeting, risk management, and business continuity planning. This is especially important when your business adds new cloud apps, opens a second site in Northeast Illinois, or changes compliance obligations. Our article on building an annual IT planning calendar is a useful framework for that process.
A simple example of retention planning
Consider a 35-person nonprofit with Microsoft 365, a donor database, shared finance files, and a small on-premises file server.
A practical retention approach might be:
- Daily Microsoft 365 and server backups for 30 days
- Weekly backups for 12 weeks
- Monthly backups for 12 months
- Annual finance and donor data archives retained according to policy and legal guidance
This gives the organization flexibility for accidental deletion, delayed issue discovery, audit preparation, and seasonal reporting without treating every file and every system the same way forever.
What Platinum Systems recommends
At Platinum Systems, we encourage businesses to treat backup retention as part of technology governance and operational planning, not as a default setting left over from initial setup. The right policy should reflect how your business works, what data matters most, and what downtime would actually cost.
That usually means reviewing:
- Business-critical applications
- Recovery time expectations
- Recovery point expectations
- Compliance and contract obligations
- Storage cost trends
- Testing and documentation practices
It also means revisiting the policy over time. A retention plan that fit a 10-person office may be inadequate for a growing firm with multiple locations, remote staff, and heavier cloud dependence.
Conclusion
A backup retention policy tells your business how long backup data should be kept so you can recover from problems without overspending or creating unnecessary complexity. The best retention period is the one that matches your real operational needs, compliance obligations, and tolerance for downtime.
If you’re ready to strengthen your technology, reduce risk, and plan for the future, contact Platinum Systems to schedule a technology strategy discussion. We can help you evaluate whether your current backup approach supports the way your business actually operates.