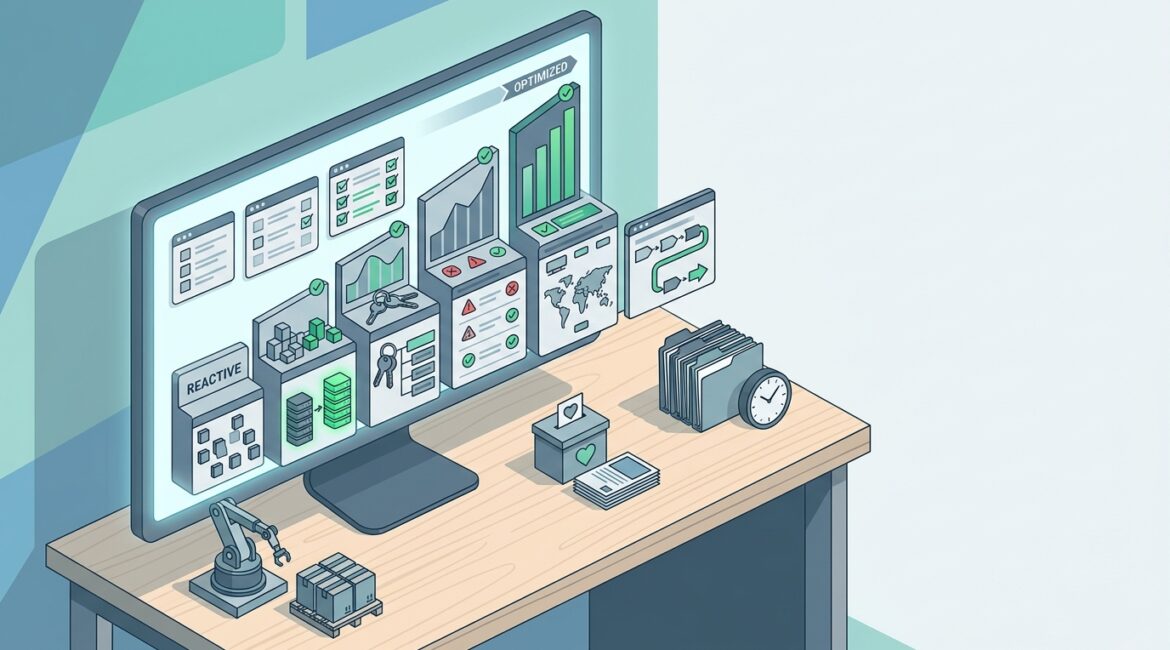
A cybersecurity maturity model is a framework that helps you measure how developed your security practices really are. It shows whether your business is operating in a reactive mode, following repeatable processes, or making security part of long-term planning and day-to-day operations.
For business leaders, the value is simple. A maturity model helps you see where you stand, what gaps matter most, and what to improve next without guessing or overspending.
What a cybersecurity maturity model means in plain English
Most organizations have some security tools in place. They may use antivirus software, require passwords, and back up data. That does not automatically mean security is mature.
Maturity is about consistency. If one employee follows the rules, one manager approves software, and one IT person remembers to review alerts, that is not a mature process. A mature organization has clear standards, documented steps, assigned ownership, and regular review.
Think of it like financial controls. A company is not financially disciplined just because it has a bank account and accounting software. It becomes disciplined when approvals, reporting, budgeting, and audits happen on a defined schedule. Cybersecurity works the same way.
Why maturity matters to business leaders
Security maturity affects more than breach headlines. It influences downtime, insurance applications, vendor requirements, audit readiness, and how much disruption your team faces when something goes wrong.
For example, a manufacturer in Southeast Wisconsin may lose thousands of dollars per hour if production stops because one infected workstation reaches a shared system. A nonprofit in Kenosha may not have that kind of hourly revenue loss, but it could still face donor trust issues, grant reporting problems, and days of staff disruption if email accounts are compromised.
A professional services firm may be hit differently. If attorneys, accountants, or consultants cannot access client files for even half a day, billable time disappears quickly. Ten employees losing four productive hours at an average loaded cost of $60 per hour is $2,400 in lost labor before any recovery cost is added.
Common maturity levels most businesses move through
Different frameworks use different labels, but most follow a similar progression.
Level 1: Reactive
Security depends on individual effort and urgent fixes. Passwords may be weak, software updates may happen irregularly, and documentation is limited. Problems are usually addressed after they cause disruption.
Level 2: Basic and repeatable
The business has standard tools and some policies. Multi-factor authentication may be in place, backups are scheduled, and onboarding and offboarding are more consistent. This is a meaningful improvement, but coverage may still be uneven.
Level 3: Defined and managed
Security processes are documented, assigned, and reviewed. Access control is based on job roles, systems are monitored, vendors are evaluated, and leadership has visibility into risk. This is often where smaller organizations begin to gain real control.
Level 4: Measured and proactive
The business tracks performance, tests recovery, reviews trends, and improves controls before issues become incidents. Technology decisions are tied to business priorities, budget planning, and operational risk.
Level 5: Strategic and optimized
Security is built into governance, purchasing, training, and long-range planning. Leadership uses security data to guide decisions, and the organization adjusts as the business changes. At this stage, security supports growth instead of slowing it down.
How to tell where your business stands
You do not need to be a technical expert to spot maturity gaps. Start by asking practical questions about how your organization operates.
- Do we know what systems, devices, apps, and data we have?
- Are security tasks documented, or do they live in one person’s head?
- Can we remove access quickly when an employee leaves?
- Are backups tested, or just assumed to be working?
- Do we review admin access, software sprawl, and vendor connections regularly?
- Can leadership see security priorities in business terms such as downtime, cost, and risk?
If several of those answers are no, your business is likely in an early maturity stage. That is common, especially for growing organizations that added tools over time without a clear plan.
A structured review such as an IT health check can help uncover these gaps before they turn into expensive surprises.
The areas a maturity model usually evaluates
A good maturity review looks beyond one security product. It examines how your organization manages risk across people, process, and technology.
Identity and access
This includes passwords, multi-factor authentication, admin rights, role-based access, and account cleanup. Many incidents start here because access is too broad or old accounts remain active.
Devices and infrastructure
Are laptops, servers, firewalls, and wireless systems standardized and maintained? Are unsupported devices still in use? Older equipment often creates both security and reliability issues.
Data protection
This covers backups, file access, retention, encryption, and recovery testing. A mature business knows which data matters most and protects it accordingly.
Monitoring and response
If something suspicious happens, will anyone know quickly? Maturity includes alerting, review, escalation paths, and a clear response plan.
Policies and governance
Written standards matter because they create consistency. Without them, every manager and employee makes separate decisions about software, file sharing, and access.
Training and culture
Employees do not need to become security experts, but they do need practical guidance. Mature organizations make secure behavior part of normal work.
What low maturity looks like in real businesses
In a small manufacturing company, low maturity might mean one shared admin password for several systems, old PCs on the shop floor, and no tested recovery process for production files. The business may run fine for months, then lose a full day when a failed device or malware event spreads farther than expected.
In a nonprofit, it may look like former staff accounts still active in Microsoft 365, donor files stored across personal drives, and inconsistent approval for new software. That creates risk without anyone intending to cut corners.
In a professional services firm, low maturity often shows up as too many exceptions. One partner uses personal cloud storage, another shares credentials with an assistant, and a third delays laptop replacement for years. Each decision seems small until a client request, audit, or incident exposes the weakness.
Improving maturity does not mean buying everything at once
One of the biggest misconceptions is that maturity requires a massive security overhaul. In reality, most businesses improve by fixing the basics in the right order.
Practical first steps often include:
- Building a current inventory of devices, software, accounts, and vendors
- Standardizing identity security with multi-factor authentication and stronger access controls
- Cleaning up old accounts and excess permissions
- Testing backups and recovery steps
- Documenting key systems and responsibilities
- Creating a yearly review cycle for security, replacements, and policy updates
That is one reason planning matters so much. An annual roadmap keeps improvements manageable and tied to budget decisions. Our article on how to build an annual IT planning calendar for your business outlines a practical way to schedule those decisions before they become urgent.
How maturity supports budget control and efficiency
Higher maturity usually lowers avoidable cost. Not because incidents disappear entirely, but because the business spends less on emergency fixes, downtime, duplicate tools, and rushed replacements.
Consider a 25-person office with inconsistent device standards. If four aging laptops fail in the same quarter, the business may face rush purchases, employee downtime, and support labor all at once. A mature lifecycle plan spreads those costs out and reduces disruption.
The same applies to software and cloud services. When access, ownership, and approvals are defined, businesses are less likely to pay for overlapping apps or leave former employee accounts active for months.
Where many small and midsize businesses really stand
Most small and midsize organizations in Southeast Wisconsin and Northeast Illinois are not starting from zero. They usually have some good tools in place. What they often lack is consistency, documentation, and a business-level plan.
That means they may be stronger than they think in a few areas and weaker than they realize in others. A company may have strong email filtering but poor vendor access control. Another may have reliable backups but weak account management. Maturity helps make those tradeoffs visible.
What to do next if you are unsure
If you are not sure where your organization stands, start with a structured assessment. Look at your environment as a business system, not just a collection of devices and licenses.
Review your inventory, access controls, backup testing, documentation, and leadership reporting. Compare what exists to what your operations actually depend on. If your environment has grown organically, it may also be worth reviewing how technology decisions are governed over time. Our post on technology governance for small businesses is a useful next step.
A cybersecurity maturity model is not about chasing a perfect score. It is about building a business that is easier to protect, easier to support, and less likely to be disrupted by preventable problems.
If you’re ready to strengthen your technology, reduce risk, and plan for the future, contact Platinum Systems to schedule a technology strategy discussion.
Platinum Systems works with organizations that want practical guidance, clear priorities, and a more proactive approach to technology. If you would like help evaluating your current security maturity and building a smarter plan, we would be glad to talk.