A disaster recovery test is a planned exercise that proves whether your backups, systems, and people can actually restore operations after a disruption. Most businesses should run some form of disaster recovery test at least once or twice a year, with smaller checks happening more often when systems, staff, or business processes change.
If you only know that backups exist, but you have never tested whether they can be restored quickly and correctly, you do not really know how prepared you are. Testing turns assumptions into facts.
What a disaster recovery test actually means
In plain English, a disaster recovery test is a practice run. Your business simulates a problem such as a server failure, ransomware event, internet outage, deleted data, or loss of access to a cloud application, then confirms whether recovery steps work the way they are supposed to.
The goal is not to create drama. The goal is to answer practical questions:
- Can we restore critical files and systems?
- How long does recovery actually take?
- Who is responsible for each step?
- Are our backups complete and usable?
- Can employees keep working during the disruption?
- Do our vendors, tools, and documentation support recovery?
A written recovery plan is useful, but a tested recovery plan is what protects the business.
Why businesses skip testing and why that creates risk
Many organizations assume that if they are paying for backup software or cloud services, recovery is covered. That is a risky assumption. Backups can fail silently, permissions can change, servers can be misconfigured, and key staff members may not know the current process.
We often see this issue with growing manufacturers, nonprofit organizations, and professional service firms in Southeast Wisconsin and Northeast Illinois. They have a mix of on-premise systems, cloud apps, shared files, and vendor-managed tools, but no recent proof that everything can be restored in the right order.
That gap matters because the business impact of a failed recovery is rarely limited to IT. It affects payroll, production schedules, donor records, billing, client deadlines, and customer communication.
What a disaster recovery test should include
A useful test should focus on business priorities, not just technical steps. Start with the systems that would hurt the most if they were unavailable for a day.
Core areas to test
- Backup restoration for files, servers, and cloud data
- Recovery time to see how long restoration actually takes
- Recovery point to confirm how much data could be lost between backups
- Access and permissions so the right people can log in after recovery
- Dependencies such as internet, firewalls, line-of-business apps, and vendor systems
- Documentation accuracy including passwords, contacts, diagrams, and step-by-step procedures
- Communication so employees and leadership know what to do during an outage
For example, a CPA firm may need to restore its tax software, document management system, and shared client files in a specific order. A manufacturer may need ERP access, production scheduling, barcode systems, and shipping workstations restored before the office file share. A nonprofit may prioritize donor databases, Microsoft 365, and accounting systems so fundraising and operations can continue.
Different types of disaster recovery tests
Not every test has to be a full shutdown simulation. In fact, most businesses benefit from a mix of test types.
Checklist or documentation review
This is the simplest option. Your team reviews the recovery plan, vendor contacts, system inventory, and backup scope to make sure everything is current. It is useful, but it does not prove recovery will work.
Tabletop exercise
This is a guided discussion where leaders and key staff walk through a realistic outage scenario. It helps clarify responsibilities, decisions, and communication steps. If your team has never done one, our article on what a cybersecurity tabletop exercise is is a good companion read.
Restore test
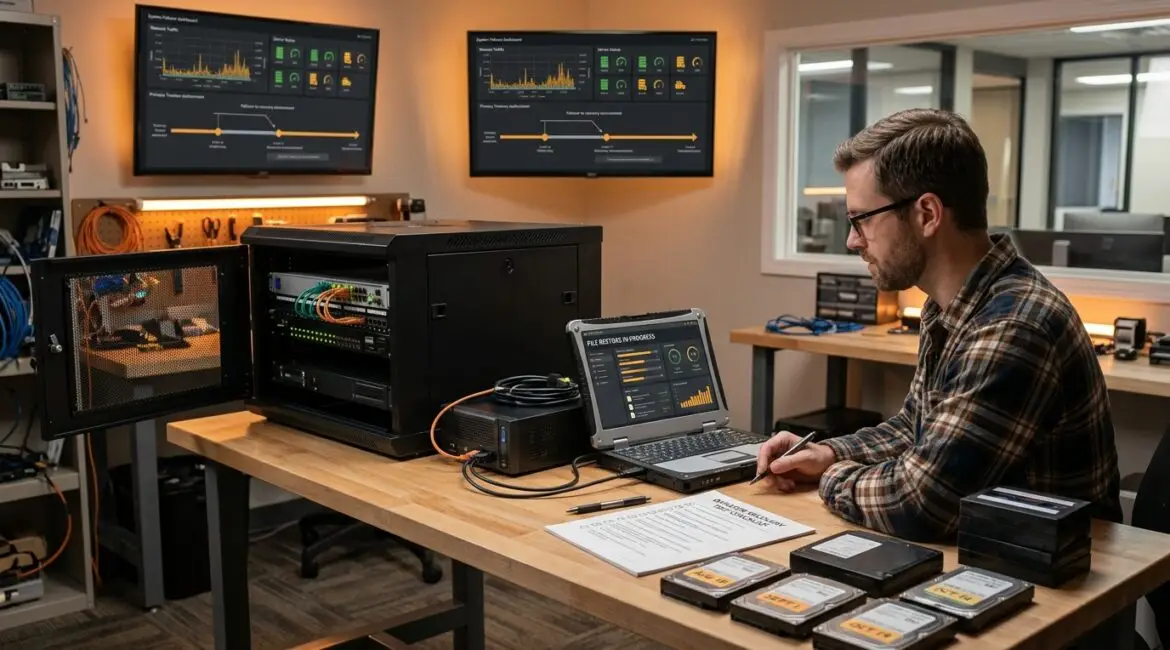
This is where you recover specific files, folders, virtual machines, or applications in a controlled environment. It is one of the most practical tests because it confirms whether backups are usable.
Failover or live recovery test
This is more advanced. You intentionally shift systems to backup infrastructure or a recovery environment to confirm business continuity under real conditions. It requires planning, but it gives the clearest picture of actual readiness.
How often should you run a disaster recovery test?
For many small and midsize businesses, a good starting point is:
- Quarterly backup restore tests for critical systems or data sets
- Every 6 to 12 months for a broader disaster recovery test
- After major changes such as server replacements, cloud migrations, software rollouts, office moves, or vendor changes
The right schedule depends on how costly downtime would be for your organization. If one hour of outage causes missed shipments, lost billable time, or service delays, annual testing alone may not be enough.
A practical way to decide frequency
Ask three business questions:
- How long can we operate without this system?
- How much data can we afford to lose?
- What would one day of disruption cost us in revenue, payroll, delays, or reputation?
Consider a 25-person professional services firm with an average loaded labor cost of $45 per hour. If a file server outage stops most work for six hours, that is roughly $6,750 in lost productivity alone, before client delays or catch-up time. For a manufacturer, a half day of downtime could mean missed production runs, overtime, delayed shipping, and strained customer relationships. For a nonprofit, losing donor database access before a campaign deadline could directly affect fundraising results.
When leaders see recovery testing in business terms, the value becomes much clearer.
Signs your current testing is not enough
- You have backups, but no one has restored from them recently
- Your recovery plan depends on one employee or one vendor contact
- You are not sure which systems are most critical
- Cloud applications are assumed to be fully protected without separate recovery planning
- Your documentation is outdated
- You have added locations, remote staff, or new software without updating recovery procedures
- You have never timed how long restoration takes
If any of these sound familiar, the issue is usually not a lack of effort. It is a sign that the business has outgrown informal recovery planning.
Common mistakes that weaken disaster recovery
Testing only backups, not operations
Restoring a file is not the same as restoring the business. You need to know whether employees can access systems, whether workflows still function, and whether dependent tools come back online in the right order.
Ignoring cloud recovery
Many organizations assume Microsoft 365, file sharing platforms, or SaaS applications remove the need for testing. They do not. You still need to verify retention, restoration options, access controls, and administrative recovery steps. Our article on building a more resilient Microsoft 365 environment covers this in more detail.
No ownership outside IT
Disaster recovery is not only an IT responsibility. Operations, finance, leadership, and department managers all need defined roles. Someone has to decide what comes back first, who communicates with staff, and how the business works during the gap.
Not updating the plan after changes
Technology environments change constantly. New software, staff turnover, vendor changes, and office relocations can all make an older recovery plan inaccurate. This is one reason regular planning matters. For a broader planning framework, see how to build an annual IT planning calendar for your business.
What business leaders should ask their IT provider
If you rely on an internal team, outside IT partner, or both, ask direct questions:
- When was our last disaster recovery test?
- What exactly was tested?
- How long did recovery take?
- Were there any failures or delays?
- Which systems are considered critical?
- What is our expected downtime for each critical system?
- Are cloud platforms included in our recovery plan?
- What changes would improve recovery speed or reduce risk?
These questions help shift the conversation from vague reassurance to measurable readiness.
How Platinum Systems approaches recovery planning
At Platinum Systems, we view disaster recovery testing as part of a larger business continuity strategy. The point is not to run a test for the sake of checking a box. The point is to make sure your organization can keep operating when something goes wrong.
That means understanding which systems matter most, documenting realistic recovery steps, validating backups, and aligning the testing schedule with the cost of downtime. For businesses in Kenosha, Southeast Wisconsin, and Northeast Illinois, that often includes balancing practical budgets with real operational risk.
Conclusion
A disaster recovery test tells you whether your business can actually recover, not whether you hope it can. For most organizations, testing at least annually, with smaller restore checks throughout the year and after major changes, is a practical standard.
If you’re ready to strengthen your technology, reduce risk, and plan for the future, contact Platinum Systems to schedule a technology strategy discussion.