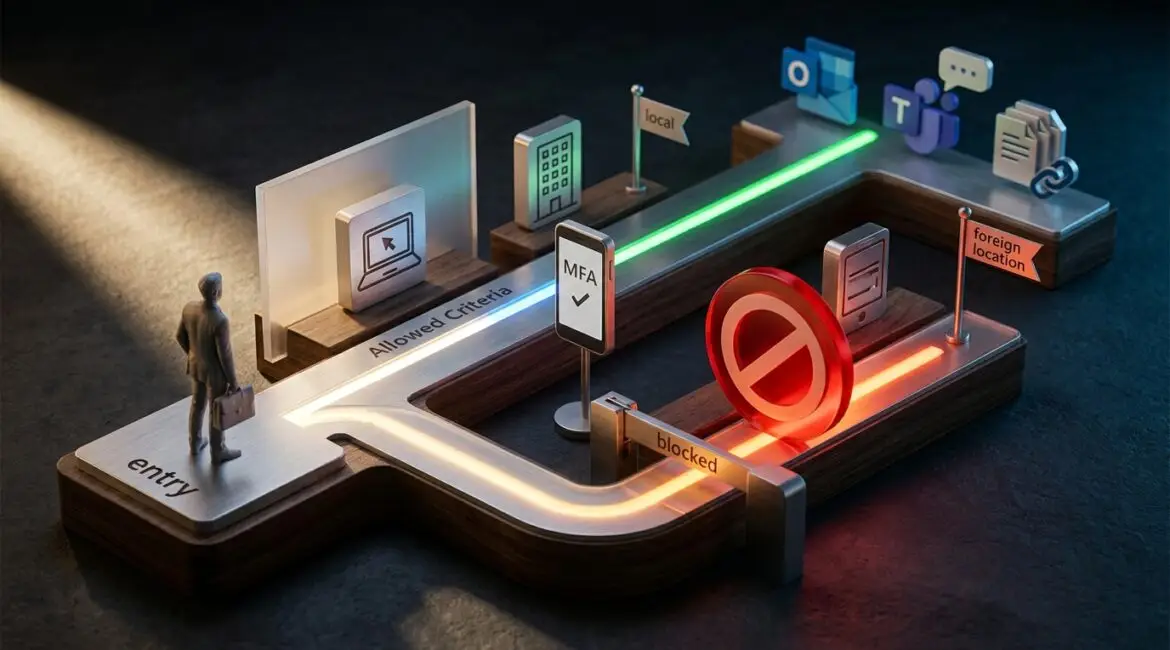
Microsoft Entra Conditional Access is a Microsoft security feature that decides whether a user should be allowed into an app or account based on conditions such as location, device health, sign-in risk, and whether multifactor authentication is completed. You should use it when you want stronger control over who can access business systems without forcing the exact same login experience on every user, every time.
For many organizations, this is one of the most practical ways to improve Microsoft 365 security. Instead of relying only on usernames and passwords, you create rules that fit how your business actually works.
What Microsoft Entra Conditional Access does in plain English
Think of Conditional Access as a gatekeeper for cloud sign-ins. It checks the situation around a login attempt, then applies the rule you set.
For example, a policy might say:
- Allow access if the employee is using a company-managed laptop
- Require multifactor authentication if the employee is signing in from a new location
- Block access if the sign-in looks suspicious
- Prevent access to sensitive apps from personal devices
That is why it is called conditional access. Access is not simply on or off. It depends on the conditions around the request.
Why business leaders should care
Most security incidents do not start with a movie-style hack. They start with a stolen password, an unmanaged device, a fake login page, or an employee trying to work around weak access controls.
If an attacker gets into a Microsoft 365 account, the damage can spread quickly. Email can be used to target customers, invoices can be altered, files can be downloaded, and internal conversations can be exposed. Even a short disruption can be expensive.
A 25-person professional services firm, for example, might lose several hours of billable time if email access has to be locked down after a compromised account. A manufacturer in Southeast Wisconsin could face shipping delays if supervisors cannot access shared files or Teams during an incident. A nonprofit may have donor information and grant records exposed, creating both trust and compliance concerns.
Conditional Access helps reduce those risks by making it harder for the wrong person, device, or session to get through.
How Conditional Access works
Microsoft evaluates a sign-in using signals it already knows about. Your business then creates policies that tell Microsoft what to do with those signals.
Common signals used in policies
- User or group: Apply stricter rules to executives, finance staff, or administrators
- Application: Protect Microsoft 365, Teams, SharePoint, Exchange, or other connected apps
- Location: Treat sign-ins from trusted offices differently from unknown countries or regions
- Device state: Check whether the device is company-managed, compliant, or known
- Risk level: Respond to suspicious sign-in behavior detected by Microsoft
- Client app: Limit older authentication methods that are easier to abuse
Common actions a policy can take
- Allow access
- Block access
- Require multifactor authentication
- Require a compliant or managed device
- Require password reset in higher-risk situations
- Limit session behavior, such as restricting downloads in a browser session
If you have already read our article on how to use Microsoft Entra ID to improve business security, Conditional Access is one of the strongest tools inside that broader identity strategy.
When should a business use Microsoft Entra Conditional Access?
The short answer is this: use it when your business depends on Microsoft 365 or other cloud apps and you need better control than passwords alone can provide.
Good times to implement it
- Your team works remotely, travels, or signs in from multiple locations
- You store sensitive files in Microsoft 365, SharePoint, or OneDrive
- You have finance, HR, leadership, or donor data that needs tighter protection
- You want to require MFA without applying the same rule to every scenario
- You need to reduce risk from personal devices
- You are trying to meet cyber insurance or compliance expectations
- You have administrators or privileged accounts that need extra protection
This is especially relevant for growing organizations in Kenosha, Southeast Wisconsin, and Northeast Illinois that have moved from mostly office-based work to hybrid work. Once employees sign in from home, hotels, client sites, and mobile devices, basic login controls are usually not enough.
Practical business examples
Manufacturer with plant floor and office staff
A manufacturer may want office employees to access Microsoft 365 from managed laptops, while limiting what can be done from personal phones. Finance staff could be required to complete MFA every time they access payment systems, while plant floor kiosks might be restricted to specific apps only.
Nonprofit with staff and volunteers
A nonprofit might allow volunteers into a limited set of cloud tools but block access to donor databases unless the user is on an approved device. That keeps collaboration moving without opening every system to every account.
Professional services firm handling client records
An accounting, legal, or engineering firm can require stronger checks when someone signs in from an unfamiliar location or tries to download files from a personal device. That lowers the odds of client information leaving the business through a compromised or unmanaged endpoint.
What Conditional Access is not
It is helpful, but it is not a complete security program by itself.
Conditional Access does not replace:
- Endpoint protection
- Backup and recovery planning
- User security awareness training
- Secure file permissions
- Network monitoring
- Good lifecycle and device management
It works best as part of a broader plan. For example, if your devices are inconsistent or poorly managed, your access rules become harder to enforce. That is one reason proactive reviews such as an IT health check are valuable before rolling out stricter identity controls.
How to use it without frustrating employees
One concern business leaders often have is usability. They do not want security changes to create extra steps for every employee, every day.
That is a fair concern. The answer is not to avoid Conditional Access. The answer is to design it carefully.
Start with high-value, low-friction policies
- Require MFA for all admin accounts
- Block legacy authentication
- Require MFA for sign-ins from new or risky locations
- Require compliant devices for sensitive apps
These policies usually improve security without creating major workflow problems.
Roll out in stages
Test policies with a pilot group before applying them to the whole organization. That helps catch issues with shared devices, legacy apps, or unusual workflows before they affect everyone.
Use reporting and monitoring
Sign-in logs and policy reports show what would have happened before you fully enforce a new rule. That gives your IT team or MSP a chance to adjust safely.
This measured approach fits with the same planning mindset we discuss in how to improve cybersecurity without making employees less productive. Good security should support work, not constantly interrupt it.
Licensing and cost considerations
Conditional Access is not available in every Microsoft license tier, so licensing matters. Many businesses use it through Microsoft Entra ID P1 or Microsoft 365 Business Premium, depending on their setup and policy needs.
The licensing cost is usually far lower than the cost of a single account compromise. If a finance user account is hijacked and fraudulent messages go out to customers or vendors, the cleanup time alone can exceed months of licensing costs. Add lost staff time, outside incident response, and possible reputational damage, and the math becomes straightforward.
Common mistakes to avoid
- Turning on too much at once: This can lock out users or break needed access
- Ignoring service accounts or shared accounts: These often become weak points
- Not excluding emergency access accounts: You need a safe recovery path
- Failing to document policies: Over time, unclear rules create support issues and risk
- Leaving personal devices unmanaged while allowing broad access: This weakens the whole model
As with many Microsoft 365 controls, long-term success depends on consistency. If policies are added casually and never reviewed, configuration drift can create gaps and confusion over time.
Is it right for your business?
If your organization uses Microsoft 365, has remote or hybrid workers, stores sensitive information in the cloud, or wants better control over sign-ins, the answer is probably yes.
The real question is not whether Conditional Access is useful. It is whether it is being planned around your business operations, risk tolerance, and user workflows. A small nonprofit, a 60-user manufacturer, and a multi-office professional services firm may all need Conditional Access, but not in the exact same way.
Conclusion
Microsoft Entra Conditional Access gives businesses a practical way to control access based on real-world conditions instead of relying on passwords alone. When it is planned carefully, it reduces risk, supports hybrid work, and protects Microsoft 365 without adding unnecessary friction.
If you’re ready to strengthen your technology, reduce risk, and plan for the future, contact Platinum Systems to schedule a technology strategy discussion.