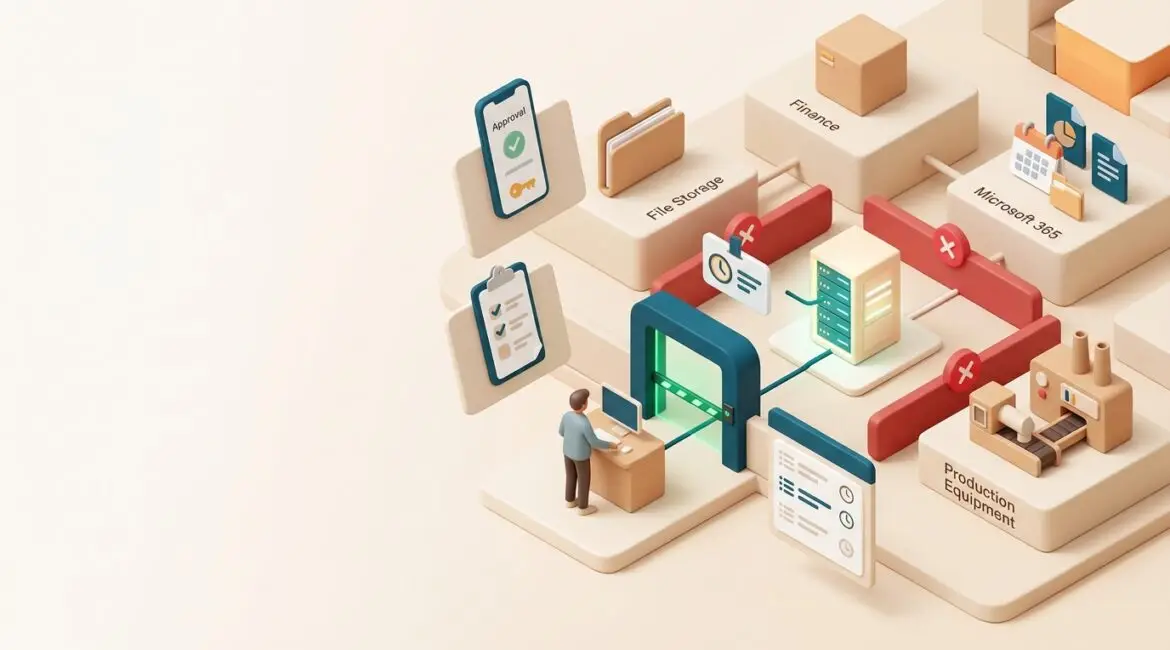
To secure business systems from third party support vendors, give vendors only the access they need, only for as long as they need it, and only through approved, monitored methods. If a software provider, copier company, HVAC contractor, ERP consultant, or outsourced developer can connect to your environment, that access needs the same planning and oversight as any employee account.
Many businesses trust vendors because they are familiar names or because access was set up years ago during an installation. That is where problems start. Old accounts, shared passwords, remote access tools, and undocumented exceptions can quietly turn vendor support into a business risk.
Why third party support access creates real business risk
Most vendors are not trying to create problems. The issue is that convenience often wins over control. A vendor may request a permanent admin account, ask to use a generic remote access tool, or keep the same credentials for years because it makes support faster.
For your business, that can lead to three expensive outcomes:
- Security exposure if a vendor account is compromised or poorly protected
- Downtime if a vendor change affects a server, firewall, business application, or production system
- Accountability gaps if no one can clearly answer who approved access, what was changed, or whether the access is still needed
A manufacturer in Southeast Wisconsin might have a machine vendor remotely connecting to production systems for maintenance. A nonprofit in Kenosha may rely on a donor database consultant. A law or accounting firm in Northeast Illinois could use outside support for line-of-business software. In each case, vendor access may be necessary, but it should never be informal.
Start with a simple rule: no unmanaged vendor access
If an outside support vendor can connect to your systems, that access should be documented, approved, and reviewed. Nothing should be left to memory or buried in an old email thread.
A good starting point is to create a list of every outside party that can touch your environment, including:
- Application vendors
- Managed print providers
- Phone system support companies
- Industrial equipment vendors
- Website developers
- Accounting or ERP consultants
- Building systems vendors with network-connected tools
If your team does not already have a reliable inventory, this is a good time to build one. A structured record of systems, accounts, vendors, and ownership makes security decisions much easier. Platinum Systems often recommends treating vendor access as part of a broader documentation effort, similar to the discipline described in network documentation.
Use the least access necessary
One of the most common mistakes is giving vendors broad administrator rights because it seems easier. In practice, that creates unnecessary risk. A vendor supporting one application usually does not need access to your whole server environment, your Microsoft 365 tenant, or your firewall.
Instead, define access around the specific task:
- Which system does the vendor need to reach?
- What level of permission is required?
- Does access need to be available all the time, or only during scheduled support?
- Can the vendor use a named account instead of a shared login?
For example, if a payroll software consultant only needs access to one application server once per quarter, a permanent domain admin account would be excessive. A time-limited account with multi-factor authentication is far safer and still practical.
Require secure remote access methods
Not all remote access is equal. Consumer-grade tools, shared credentials, and direct internet exposure create avoidable problems. Vendors should connect through approved methods that your business can control.
That usually means:
- Multi-factor authentication for every vendor account
- Named user accounts, not generic shared logins
- Remote access through a secured gateway, VPN, or controlled remote administration platform
- Logging of sign-ins and activity when possible
- Restrictions by device, time, or source network when appropriate
If you want a deeper look at this topic, secure vendor access often overlaps with the same controls used for secure remote administration. The principle is simple. Fast support is useful, but not if it bypasses the controls your business depends on.
Remove shared passwords and informal workarounds
Many vendor relationships begin with a quick fix. Someone shares the admin password. A remote desktop port gets opened temporarily and never closed. An old employee account gets repurposed for a consultant. Years later, nobody remembers why it still exists.
These shortcuts are common, especially in growing businesses, but they create long-term risk. They also make support harder to manage when staff changes, audits happen, or an incident needs investigation.
Replace those workarounds with better controls:
- Use individual vendor accounts
- Store credentials in an approved enterprise password management system
- Rotate passwords when personnel or vendors change
- Disable accounts immediately when support contracts end
- Review all standing access at least quarterly
Set approval and change rules before vendors touch production systems
Access control is only part of the picture. You also need a process for what vendors are allowed to change.
A support vendor should not be making major updates to a critical server, firewall, accounting platform, or manufacturing system without clear approval. Even well-intentioned changes can cause downtime if they are done without coordination.
Practical approval rules to put in place
- Require a business contact and technical contact for every vendor
- Define which changes need pre-approval
- Schedule non-urgent work during low-impact hours
- Confirm backups before major updates
- Document what changed, when, and why
This matters because the cost of a small mistake can add up quickly. If a 25-person professional services firm loses access to its document management system for half a day, the direct labor loss alone can be several thousand dollars. If a manufacturer has a two-hour interruption on a production line because a vendor changed a network setting without coordination, the cost can be much higher.
Monitor vendor activity and review it regularly
You cannot manage what you cannot see. Businesses often approve vendor access once and never revisit it. That is how unnecessary accounts stay active for years.
At a minimum, review:
- Which vendors currently have access
- Which accounts have not been used recently
- Whether multi-factor authentication is enabled
- Whether permissions still match current support needs
- Whether logs show unusual connection times or failed sign-in attempts
This is also where broader visibility helps. If your organization lacks clear insight into who and what is connecting across the environment, improving network visibility can help you spot access that should be tightened or removed.
Include vendor access in your business continuity planning
Third party support is often critical during emergencies. If a server fails, a cloud application breaks, or a specialized system stops working, you may need a vendor quickly. But emergency access should still follow a plan.
Your business continuity process should answer questions like:
- Who can approve urgent vendor access after hours?
- How will the vendor connect securely during an outage?
- What happens if the primary contact at the vendor is unavailable?
- Do you have current documentation for key vendor-supported systems?
This is one reason proactive planning matters so much. Vendor access should be part of your annual review cycle, not something handled only when a problem appears. A structured planning process, like the one outlined in an annual IT planning calendar, helps prevent rushed decisions and forgotten risks.
What good vendor access management looks like in practice
A well-managed business environment does not block vendors from doing their jobs. It gives them a clear, secure path to do approved work without exposing the rest of the organization.
In practice, that usually looks like this:
- Every vendor has an identified business owner
- Access is tied to named accounts with multi-factor authentication
- Permissions are limited to the systems being supported
- Remote access is routed through approved tools
- Changes are documented and reviewed
- Unused access is removed on a schedule
That approach reduces risk, but it also improves operations. Your team spends less time chasing old credentials, sorting out vendor confusion, or recovering from preventable outages. Support becomes more predictable, and accountability improves.
Conclusion
Securing business systems from third party support vendors comes down to control, visibility, and planning. If a vendor can access your environment, that access should be limited, documented, monitored, and reviewed just like any other critical business risk.
If you’re ready to strengthen your technology, reduce risk, and plan for the future, contact Platinum Systems to schedule a technology strategy discussion.
Platinum Systems helps organizations across Southeast Wisconsin and Northeast Illinois make practical technology decisions that support security, reliability, and long-term business goals.